
Navigating the Data Privacy Maze: A Guide to Compliance for Organizations
Today's data-driven organizations collect an enormous amount of personal information — and that authority comes with real responsibility. The good news is that a growing body of regulation exists specifically to hold organizations accountable for protecting that data. The challenging part is that this landscape has become genuinely complex: it's no longer just a handful of familiar acronyms like GDPR and CCPA. By 2026, 15 or more U.S. states have their own comprehensive privacy laws, each with subtly different thresholds, rights, and enforcement mechanisms.
Don't panic. This guide walks through the regulations that matter most today and the core compliance principles that hold true across nearly all of them.
Understanding the Landscape (It's Bigger Than "The Big Three")
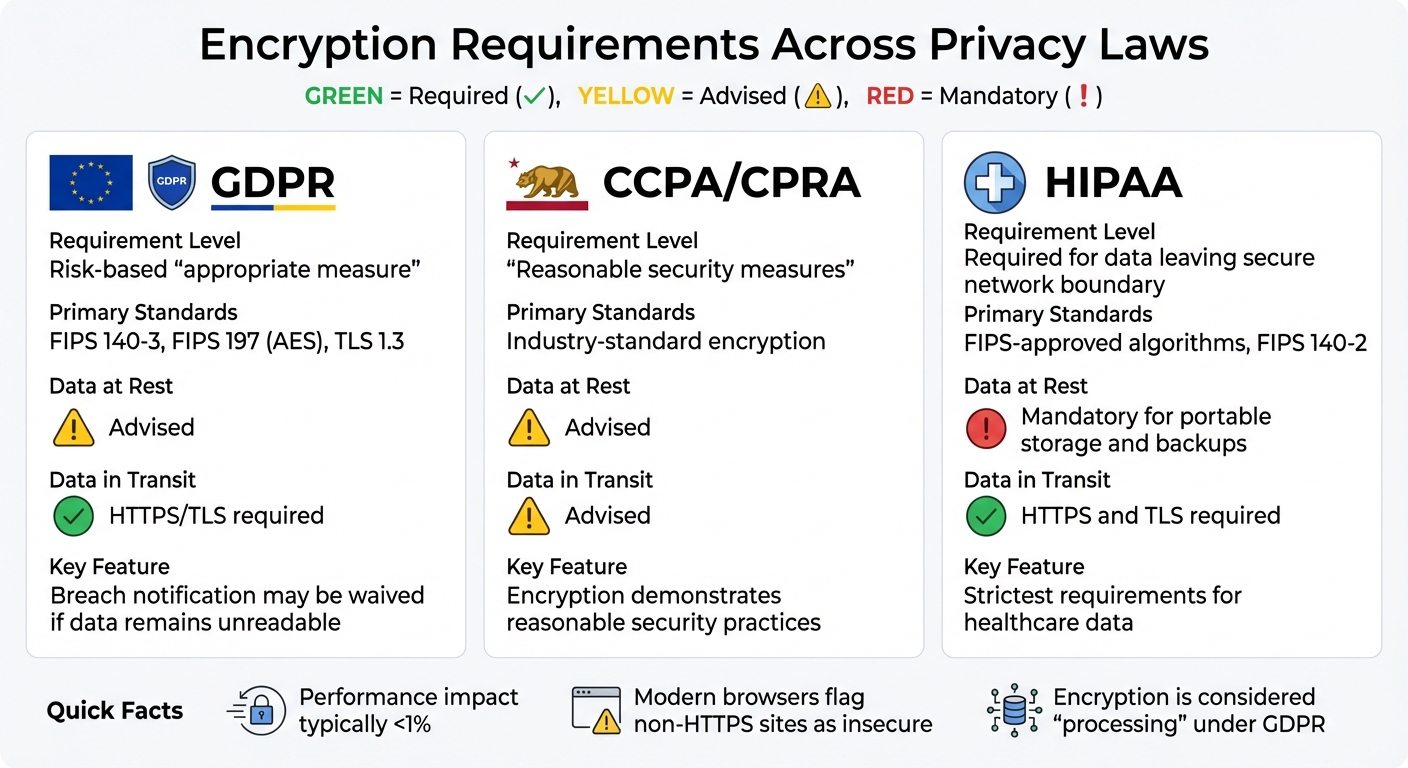
GDPR (General Data Protection Regulation)
Enacted by the European Union, the GDPR remains the most comprehensive data privacy law in force globally. It applies to any organization worldwide that processes the personal data of EU residents, regardless of where that organization is based. GDPR grants individuals wide-ranging rights over their data, including the ability to access, correct, erase, and restrict processing of their information. Its consent model is notably strict — generally requiring clear, opt-in consent rather than a default of collection with an opt-out option.
CCPA / CPRA (California Consumer Privacy Act)
California's law, since expanded by the California Privacy Rights Act (CPRA), remains the most influential U.S. privacy law and the country's only comprehensive statute with a dedicated regulator (the California Privacy Protection Agency) and a private right of action for certain data breaches. It applies to businesses that meet any of several thresholds — generally, handling personal data of at least 100,000 California residents or households, or deriving more than half of annual revenue from selling or sharing personal information.
Importantly, California continues to actively expand its requirements: 2026 updates added new rules covering automated decision-making technology, high-risk data processing, mandatory cybersecurity audits, and data broker obligations. Enforcement has also sharpened — the California Privacy Protection Agency issued a record $1.35 million settlement in one case, then surpassed it just months later with a $2.75 million settlement over opt-out failures.
HIPAA (Health Insurance Portability and Accountability Act)
HIPAA remains the primary U.S. law protecting individually identifiable health information ("protected health information," or PHI). It applies specifically to covered entities — health plans, healthcare clearinghouses, and healthcare providers — along with their business associates. Unlike GDPR or CCPA, HIPAA is sector-specific rather than general-purpose, so an organization outside healthcare typically won't need to comply with it directly, even if it handles large volumes of other personal data.
The Rapidly Growing State Privacy Law Patchwork
This is the part of the landscape that's changed the most. As of 2026, roughly 15 to 20 U.S. states have enacted comprehensive privacy laws of their own — including Virginia, Colorado, Connecticut, Utah, Texas, Delaware, Iowa, and, as of January 1, 2026, Indiana, Kentucky, and Rhode Island, with Arkansas following in July 2026.
This matters more than it might seem. A privacy program built purely to satisfy GDPR is not automatically sufficient for U.S. operations — GDPR's opt-in consent model differs meaningfully from CCPA's opt-out approach, and individual state requirements (like recognizing Global Privacy Control signals, or specific disclosure categories) aren't automatically covered by a European-style compliance program. Many of these newer state laws also carry real teeth: enforcement is exclusive to state attorneys general, with civil penalties commonly ranging from $7,500 to $10,000 per violation, and several states' initial "cure periods" (grace windows before penalties apply) have already expired or are expiring through 2026 — meaning the safety net many organizations relied on early on is disappearing.
The practical takeaway: if your organization operates nationally or handles data from residents in multiple states, "comply with California" is a reasonable baseline, but it is no longer the finish line.
The Path to Compliance: Core Principles That Hold Across Regulations
While the specifics vary by law, a set of core principles underpins nearly all data privacy compliance work:
- Transparency. Be upfront about what data you collect, why you collect it, and how you use it. Maintain a clear, accessible privacy policy — and keep it updated as your practices or applicable laws change, since an outdated policy is itself a compliance gap.
- Consent. Obtain clear, unambiguous consent before collecting or processing personal data. The specific mechanism matters: GDPR generally expects opt-in consent, while many U.S. state laws are built around opt-out rights instead. Don't assume one model satisfies both.
- Data minimization. Collect only the personal data genuinely necessary for a legitimate business purpose. Beyond being good practice, minimizing collection also shrinks your exposure if a breach ever occurs — you can't lose data you never collected.
- Data security. Implement robust technical and organizational measures to protect personal data from unauthorized access, disclosure, alteration, or destruction. Several 2026 state law updates now explicitly require formal risk assessments and, in California's case, mandatory cybersecurity audits for certain organizations.
- Data breach response. Have a tested incident response plan ready before you need it — one that includes promptly notifying affected individuals and regulators, and concrete steps to contain and mitigate damage. Notification timelines and requirements vary by jurisdiction, so know which rules apply to your specific footprint.
- Data inventory and mapping. This has become increasingly essential as the regulatory landscape has grown: maintain a clear, accurate map of what personal data you collect, where it's stored, how it moves through your systems, why it's processed, and who has access. Without this foundation, answering a regulator's questions — or a consumer's deletion request — becomes guesswork.
Compliance Is a Continuous Process, Not a Checklist
Perhaps the most important shift in this space: privacy compliance has moved from something organizations could treat as "get it right once" to something requiring ongoing governance. New state laws are still being enacted, existing ones are being amended (California alone updates its requirements almost annually), and enforcement is intensifying across the board — including a settlement exceeding $1 billion against a major technology company under Texas's privacy law.
Review your privacy policies and practices regularly, track new legislation in states where you operate or have customers, and treat your compliance program as something that evolves alongside the law — not something you finish and file away.
By taking transparency, consent, minimization, security, and breach preparedness seriously — and staying current as the legal landscape keeps expanding — your organization can build genuine user trust while navigating this complexity with confidence.
Frequently Asked Questions
Do I need to comply with GDPR if my company isn't based in the EU? Yes, if you process the personal data of EU residents, regardless of where your organization is physically located. GDPR's territorial scope extends to any business offering goods or services to people in the EU.
Is complying with CCPA enough to cover all U.S. state privacy laws? Not necessarily. While California compliance provides a strong baseline, other states have their own specific requirements — different consumer rights, different thresholds, and different enforcement mechanisms — that aren't automatically satisfied by a CCPA-focused program.
How many U.S. states have comprehensive privacy laws as of 2026? Roughly 15 to 20 states now have comprehensive privacy statutes in effect, with Indiana, Kentucky, and Rhode Island joining in January 2026, and Arkansas following in July 2026.
Does HIPAA apply to every business that handles health-related data? No. HIPAA specifically applies to covered entities — healthcare providers, health plans, and healthcare clearinghouses — and their business associates. A general business handling some health-adjacent data outside that structure may still need to comply with other privacy laws instead.
What happens if a state's "cure period" for privacy violations expires? Once a cure period expires, organizations generally lose the grace window to fix a violation before facing enforcement penalties. Several states' cure periods have already expired or are expiring through 2026, meaning immediate enforcement is now possible in more jurisdictions than before.